

Cloudflare & data sovereignty - a contradiction?
 Marc AchsnichTeam Lead · synaigy
7 min read
Cloudflare & data sovereignty - a contradiction in terms? We say no.
Security of personal data is a top priority for us — whether that's our employees', our customers', or our customers' customers' data. Though internet often gets linked with "anonymity", personal data frequently leaks through in practice — e.g. to third-party providers. This includes cookie identifiers, IP addresses, or browser data.
In this article, you'll learn how Cloudflare complies with GDPR and which European data protection rulings need to be considered. You'll also learn what the Data Localisation Suite is about and how it gives you control over the review and storage of your data.
This article reflects our opinion and is not legal advice.
Personal data is an important asset that needs protecting. In the age of an anonymous internet, there's a huge amount of data that can be traced back to a specific individual. Personal data includes, among other things:
Name and surname
Private address
Email address
Cookie identifier
IP address
Browser data
The latter in particular is data that a Content Delivery Network (CDN) knows about the person and can therefore identify which internet addresses a person has accessed with which browser or mobile device. However, this data is subject to strict guidelines.
European rulings on data protection
But why should this not be secure with Cloudflare? Cloudflare's headquarters is in San Francisco, California, United States of America, and it stores data, among other things, on servers in America. In recent months and years there have been various rulings and court decisions that, from a legal standpoint, view the use of providers outside the EU as highly contentious.
Schrems II
On 16 July 2020, the CJEU declared the Privacy Shield agreement between the USA and Europe invalid. This was based on the fact that the agreement cannot effectively protect citizens within Europe from data being accessed by the American intelligence services. As a result, there is currently no legally compliant basis for secure data transfer to the USA.
CLOUD Act
Through Cloud Act (Clarifying Lawful Overseas Use of Data Act), law enacted in America on 23.03.2018 obligate American providers to give US authorities access to stored data even if storage not happen in USA. Right of objection for providers apply only for citizens of countries that signed Cloud Act with America. This however so far only done by Great Britain and thus not apply e.g. for citizens of Germany.
Foreign Intelligence Surveillance Act (FISA)
With FISA (Foreign Intelligence Surveillance Act) law was created in America allowing US government to request communications of non-US citizens located outside United States for foreign intelligence service. This regulation is used for purpose of monitoring content of communications based on features like email addresses linked to intelligence targets.
Against this backdrop, it's advisable to weigh up and reconsider every use carefully.
What data does Cloudflare store?
Cloudflare generally only forwards data that is controlled by website operators. So the content is not determined by Cloudflare, but always by the website operator itself. Cloudflare may also collect certain information about the use of our website and processes data sent by us or for which Cloudflare has received corresponding instructions. In most cases, Cloudflare receives data such as IP address, contact and protocol information, security fingerprints and performance data for websites. Log data helps Cloudflare, for example, to detect new threats.
For security reasons, Cloudflare also uses a cookie. The cookie (__cfduid) is used to identify individual users behind a shared IP address and apply security settings for each individual user. It's important to know that this cookie does not store any personal data, but is absolutely necessary for the Cloudflare security functions and cannot be disabled.
Cloudflare stores information primarily in the USA and the European Economic Area. Cloudflare may transfer and access the information described above from anywhere in the world. In general, Cloudflare stores data at user level for domains on the Free, Pro and Business plans for less than 24 hours. For enterprise domains that have Cloudflare Logs enabled (formerly Enterprise LogShare or ELS), data may be stored for up to 7 days. However, if IP addresses trigger Cloudflare security alerts, exceptions to the retention periods stated above may occur.
How does Cloudflare become GDPR-compliant?
With data protection, the protection of data is always underpinned by a risk assessment, since 100% security cannot be guaranteed. The protection of data is subject to a weighing-up that takes into account sensitivity and the level of protection required, which should be low for the data Cloudflare stores, as long as no special context (see especially sensitive data, etc.) is involved. Cloudflare itself, for example, cannot trace information directly back to the person, but is instead reliant on input from ISPs.
Cloudflare offers a variety of mechanisms to ensure guarantees, rights and remedies for data subjects in the EU whose data is transferred from the EU to a third country not covered by the GDPR. These include the following mechanisms:
Where the EU Commission has decided that a third country ensures an adequate level of protection, having assessed that country's rule of law, respect for human rights and fundamental freedoms, and a range of other factors;
If a controller or a processor has established binding corporate rules;
Where a controller or processor has standard data protection clauses adopted by the Commission; or
When a controller or processor has adopted an approved code of conduct or an approved certification mechanism.
Furthermore, Cloudflare relies on the Standard Contractual Clauses (SCCs) for transferring personal data to the USA, as an alternative to the Privacy Shield, which was invalidated by Schrems II. In addition, Cloudflare has committed to exhausting all legal remedies, if requested to do so, to protect customers from illegal or unconstitutional requests.
Finally, Cloudflare confirms in its biannual transparency reports that it doesn't store data that may be requested by US authorities under the Cloud Act or FISA. They also publicly confirm "never having provided any government with a feed of customer content traversing our network."
In addition to this basic protection, Cloudflare has also added a further service to its portfolio that raises protection for all Cloudflare Enterprise customers to another level.
How can customers verify that the standard contractual clauses with Cloudflare have taken effect?
Depending on the support level with Cloudflare, customers can check in different ways whether the standard contractual clauses apply to them. Enterprise customers who concluded a contract after 8 August 2019 and have not entered into a customer-specific agreement are subject to the standard DPA updated on 1 October 2020 (Enterprise Subscription Agreement). No action is required for this customer group, as the updated DPA is incorporated by reference into this version of our ESA. Customers who have concluded an individual DPA agreement with Cloudflare should contact their Customer Success Manager with any questions about their DPA. All other customers have the option of viewing the version updated in October 2020 via the Self-Service Subscription Agreement. Insofar as the processing
Personal data is governed by GDPR, the DPA contains the EU standard contractual clauses for this data. The updated data processing agreement also contains the additional security measures mentioned above. The updated standard DPA can be viewed here.
Data Localisation Suite - the extended solution for data localisation in the EU.
The Data Localisation Suite brings together a range of products that give customers control over where their data is checked and stored. This ensures data can remain as private as desired and only goes where it's meant to go.
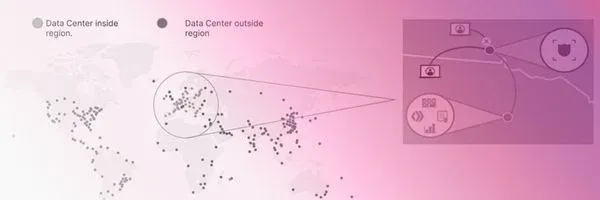
Among other things, the following setup is possible:
DDoS attacks can be detected and defended against exclusively within European data centres.
TLS encryption, WAF, CDN and Cloudflare Worker are only used on European servers.
Keyless SSL and Geo Key Manager store private SSL keys on European servers
Edge Log Delivery transfers logs directly to a partner without routing them through our own main data centre.
Cloudflare Regional Services helps decide where data should be processed, without losing the security and performance benefits of Cloudflare.
Conclusion
Despite being headquartered in the United States, Cloudflare offers protection in line with GDPR. Anyone who also wants to keep their data in Europe can use Cloudflare Enterprise together with the Data Localisation Suite to offer protection on par with European providers.
With data protection, the protection of data is always based on a risk assessment, since 100% security cannot be guaranteed. The protection of data is therefore subject to a weighing-up that takes into account the sensitivity and protection needs, which should be low for the data stored by Cloudflare. For an accurate individual assessment, you should involve your data protection officer in the risk assessment according to TIA (Transfer Impact Assessment).
Are you facing the decision to introduce Cloudflare in your company? Simply get in touch with us and we're happy to support you with the introduction. Find out how else we can support you here: https://www.synaigy.com/details/cloud-transformation
Our sources:
https://blog.cloudflare.com/empowering-your-privacy/
https://www.cloudflare.com/de-de/enterpriseterms/
https://www.cloudflare.com/de-de/terms/
https://www.cloudflare.com/de-de/cloudflare-customer-dpa/
https://www.cloudflare.com/de-de/data-localization/
https://www.cloudflare.com/de-de/press-releases/2022/cloudflare-joins-eu-cloud-code-of-conduct-achieves-new-certifications-to/
https://de.wikipedia.org/wiki/CLOUD_Act
https://de.wikipedia.org/wiki/Foreign_Intelligence_Surveillance_Act
https://de.wikipedia.org/wiki/EU-US_Privacy_Shield
https://www.srd-rechtsanwaelte.de/blog/transfer-impact-assessment/
- Marc Achsnich
Team Leadsynaigy
Show email address
Subscribe to the blog now and never miss any news
✔️free of charge ✔️weekly news ✔️expert knowledge
Please accept the corresponding cookies to view this embedded content.